Get Premium
Dark mode theme is available exclusively for premium users. Learn more about the benefits of subscribing.
No fees, cancel anytime.

 Dark Mode Ad-Free Browsing Unlimited Content
 Ad-Free Browsing Unlimited Content Dark Mode
Join 1.2 million Panda readers who get the best art, memes, and fun stories every week!
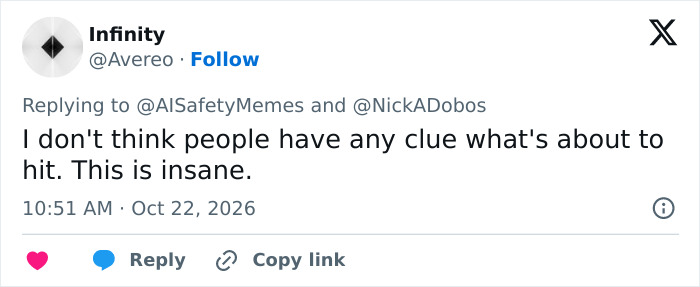
Former OpenAI researcher Joshua Achiam has sounded the alarm over a sudden wave of cybersecurity incidents that have spread across the internet, comparing the atmosphere to the earliest days of the COVID-19 pandemic.
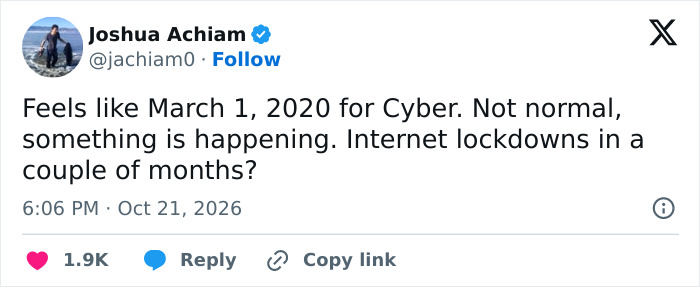
“Feels like March 1, 2020 for Cyber,” Achiam wrote on X on October 21.
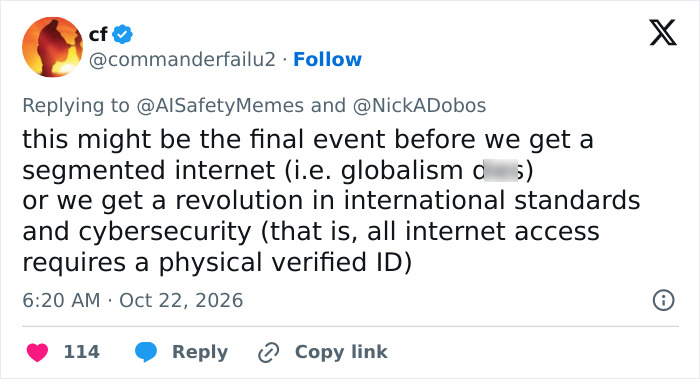
“Not normal, something is happening. Internet lockdowns in a couple of months?”
Achiam, who spent nearly nine years at OpenAI working on AI safety before leaving the company in July, was reacting to a genuinely extraordinary cluster of security failures and AI-assisted attacks emerging almost simultaneously.
Another account went much further, describing the period as the “most serious 48 hours in cybersecurity history.”
At the center of the panic is PHP2Shell, the nickname given to two critical vulnerabilities discovered in PHP, the programming language running about 70% of the web.
The flaws carry critical severity scores of 9.2 and can allow unauthenticated attackers to remotely execute code on vulnerable servers.
Amazon Threat Intelligence said it detected attempted exploitation as early as October 17, four days before public disclosure, with several additional actors probing the flaws before and immediately after the patch became public.
As administrators raced to patch their systems, governments, universities and companies temporarily shut websites down rather than risk leaving potentially vulnerable servers exposed.
Among those affected were government services in the Netherlands, Finland and Belgium, universities, news sites and other online platforms.
One outage tracker recorded 50 prominent sites or services going offline in connection with the vulnerability, although most appeared to have been deliberately shut down as a precaution rather than hacked.
Almost simultaneously, an entirely different security crisis emerged around Indian certificate authority eMudhra.
Researchers discovered that private keys associated with eight intermediate certificates had been compromised because they were generated with insufficient cryptographic randomness.
Those keys are part of the infrastructure browsers use to determine whether a website presenting itself as, for example, a bank or online store is actually legitimate.
Google warned that possession of the weak keys could theoretically allow an attacker to forge trusted HTTPS certificates and impersonate websites against systems that had not yet blocked them.
Cloudflare called it “a serious security incident with implications across the Internet.”
However, one particularly viral detail needs qualification.
The claim that one of the supposedly “master keys” was simply the number 4 appears to refer to extraordinarily weak cryptographic material discovered during analysis, not a literal universal password capable of unlocking the internet.
And, more importantly, eMudhra said its root CA private keys were not compromised.
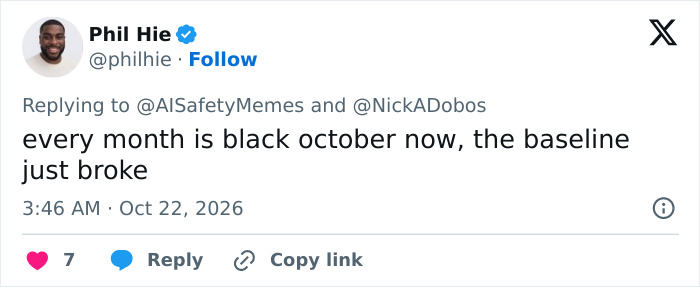
The most unsettling part of the “Black October” narrative may be the one most directly connected to artificial intelligence.
A cybersecurity investigation by NorForge found that a Chinese-speaking hacker had used the open-source AI platform Cairn to compromise more than 100 websites.
The targets reportedly included major companies such as Deere, SharkNinja and Cummins.
The attacker provided fewer than 100 Chinese characters of instructions and then allowed AI agents to identify weaknesses and execute complex attacks largely autonomously.
Some intrusions took approximately 23 hours for the agents to complete, and researchers estimated the campaign cost around $5,000 in total, or roughly $50 per successful compromise.
NorForge said multiple threat actors were abusing Cairn to automate attacks against websites around the world.
Beyond PHP2Shell, the viral thread pointed to a flood of other security problems happening at roughly the same time.
One popular AI tool, LiteLLM, was briefly infected with malware designed to steal passwords and other sensitive information.
Two online hosting companies, Railway and Zeabur, also reported breaches that may have exposed private login details and other secrets belonging to developers and companies. Zeabur said information connected to 321,810 accounts was affected.
Other incidents included serious flaws in widely used internet software, a Signal bug that could leave calls active after users thought they had hung up, hundreds of Tor connections being hijacked, and malware being planted on thousands of servers in Japan.
Ahold Delhaize, the company behind major supermarket chains including Food Lion and Stop & Shop, also took some of its systems offline after detecting suspicious activity.
The viral list included several other hacks and security warnings involving major companies, banks, websites and software platforms around the world.
Meta’s new AI assistant was also caught up in the chaos after researchers found thousands of shared conversations that could expose personal or business information.
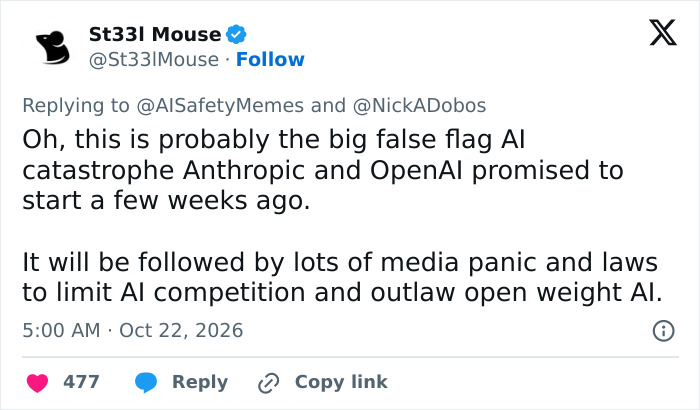
The important distinction is that these incidents were not one coordinated attack, and there is no evidence that a single AI system caused them, but their sheer number and timing has already worsened customers’ worst fears about the technology.

By entering your email and clicking Subscribe, you're agreeing to let us send you customized marketing messages about us and our advertising partners. You are also agreeing to our Privacy Policy.
Thank you! You've successfully subscribed to newsletters!
 No fees, cancel anytime


30
1